COVBEC LLP Is Building a Practical Cybersecurity Ecosystem for Businesses Facing Modern Digital Threats
As businesses become increasingly dependent on web applications, mobile apps, APIs, cloud infrastructure and interconnected digital systems, cybersecurity is no longer simply an IT requirement. A single overlooked vulnerability can expose sensitive data, disrupt operations and damage years of customer trust.
Yet for many startups, SMEs and growing organizations, cybersecurity remains difficult to approach. Enterprise security services can be expensive, internal security expertise may be limited, and one-time compliance assessments do not always reflect how quickly modern attack surfaces change.
This is the gap COVBEC LLP, an India-based cybersecurity and cyber intelligence company, is working to address.
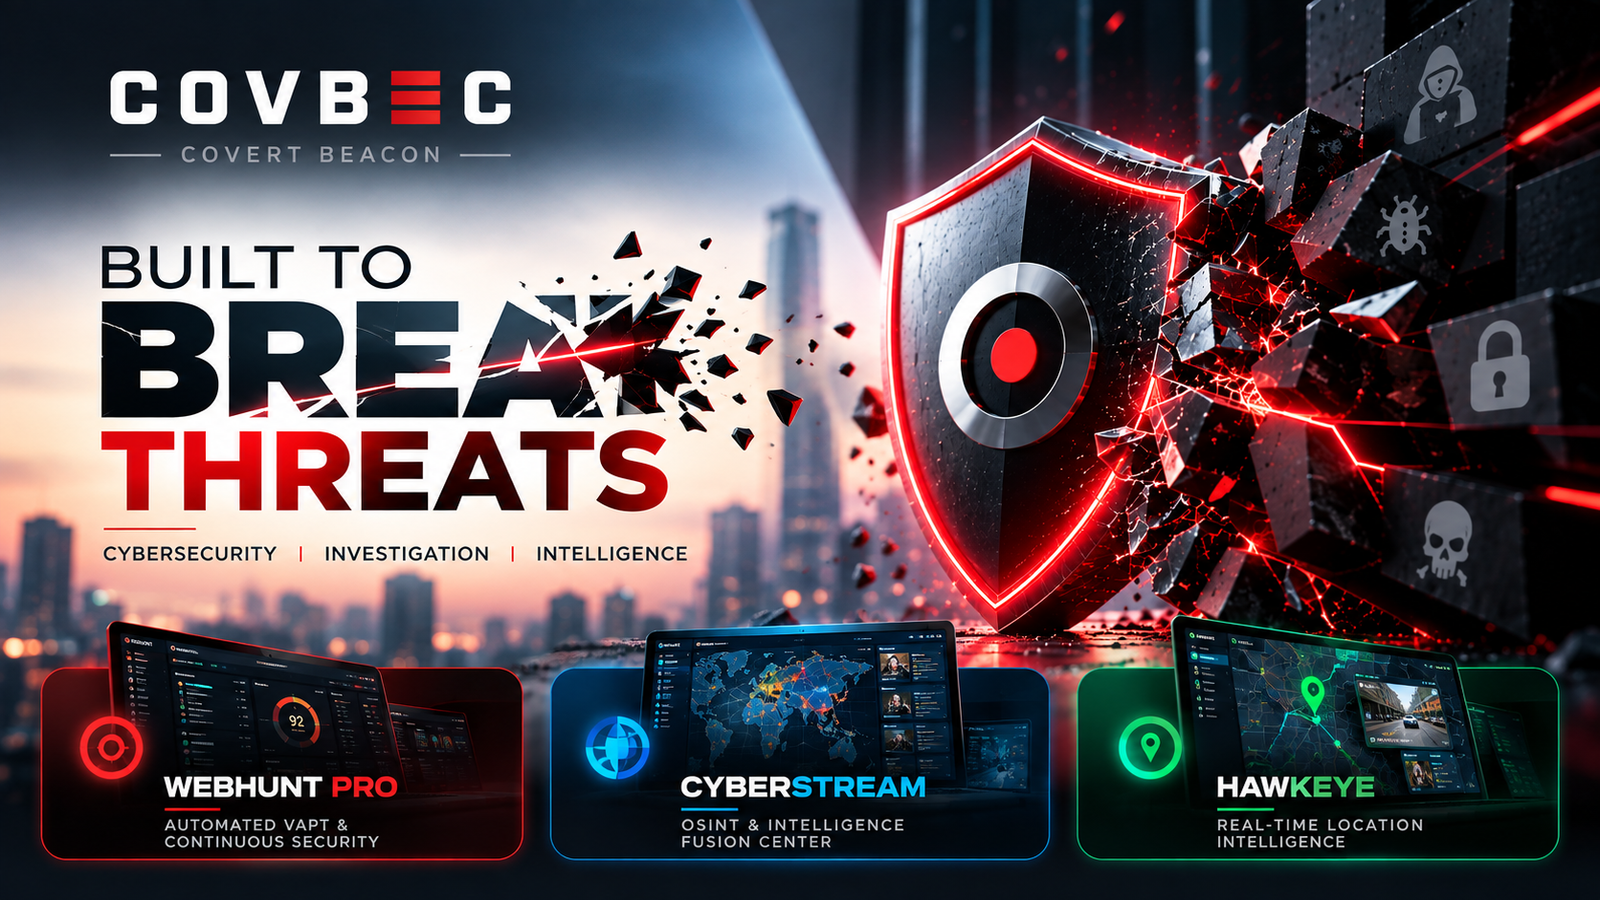
Operating with the philosophy “Built To Break Threats,” COVBEC combines offensive security, cyber investigation and specialized security research to help organizations identify weaknesses before malicious actors can exploit them.
Thinking Like an Attacker to Build Stronger Defences
Traditional cybersecurity often focuses heavily on defensive controls. COVBEC approaches security from another important perspective: understanding what an attacker could potentially discover and exploit.
Its offensive security services are designed to assess real-world exposure within an authorized scope, validate security weaknesses and provide actionable remediation recommendations.
At the centre of this approach is Vulnerability Assessment and Penetration Testing (VAPT).
COVBEC provides security testing for web applications, mobile applications, APIs, networks, infrastructure, servers and cloud environments.
Assessments can cover authentication and authorization weaknesses, insecure configurations, exposed services, API vulnerabilities, business-logic flaws and other security issues relevant to the environment being tested.
Rather than providing vulnerability data alone, COVBEC focuses on evidence-driven findings, risk context and remediation guidance that technical teams can use to strengthen their systems.
Beyond One-Time Penetration Testing
Modern applications are constantly changing.
A new API endpoint, cloud configuration, software dependency or application release can introduce risks even after a successful security assessment.
COVBEC therefore supports both traditional VAPT engagements and Penetration Testing as a Service (PTaaS) models for organizations that require recurring security assessments.
For businesses looking to evaluate security controls under more realistic scenarios, COVBEC also provides Red Team Assessments and authorized attack simulations.
The objective is not simply to discover individual vulnerabilities, but to understand how weaknesses could interact and what they could mean for an organization’s overall security posture.
From Phishing Simulation to Advanced Malware Research
Technology represents only one part of cybersecurity.
Social engineering and phishing attacks continue to target the human layer of organizations. COVBEC provides Phishing Simulation and Social Engineering Awareness services, helping organizations evaluate employee awareness through controlled scenarios and practical security education.
Another specialized capability is Malware Analysis and Reverse Engineering.
Automated malware scanners can provide useful initial indicators, but sophisticated malware may use obfuscation, encryption, anti-analysis techniques and multi-stage execution.
COVBEC provides deeper technical investigation through static and dynamic malware analysis, reverse engineering, behavioral analysis, Indicators of Compromise (IOC) identification and technical reporting.
Its research capabilities cover environments including Windows, Android, iOS and Linux, making the service relevant to enterprises, SOC teams, incident-response providers and cybersecurity companies requiring specialized malware research.
Cyber Investigation and OSINT
The growth of digital platforms has also transformed investigations.
Publicly and lawfully accessible information can be spread across numerous sources, making it difficult to convert fragmented data into meaningful intelligence.
COVBEC provides Cyber Investigation and Open-Source Intelligence (OSINT) services for authorized use cases including digital investigations, threat research, digital footprint analysis and due diligence.
The company’s broader capabilities span VAPT, Penetration Testing, Red Teaming, API Security Testing, Cloud Security, Secure Code Review, Phishing Simulation, Malware Analysis, Cyber Investigation, OSINT and Security Consulting.
Making Cybersecurity More Accessible to Growing Businesses
One of the challenges facing startups and SMEs is obtaining professional cybersecurity expertise without building a large internal security team.
COVBEC aims to bridge this gap through requirement-based engagements that can be scoped according to an organization’s application, infrastructure, risk profile and business needs.
Its services can support organizations across technology, SaaS, e-commerce, healthcare, banking and financial services, professional services and other digitally dependent sectors.
COVBEC also works toward partnerships with software development companies, IT service providers, SOC providers and technology businesses that want specialized cybersecurity capabilities to complement their existing services.
Built To Break Threats
As organizations accelerate digital transformation, cybersecurity increasingly needs to move from reactive protection to proactive risk discovery.
COVBEC’s approach is built around a straightforward principle:
Identify the exposure. Validate the risk. Strengthen the defence.
For businesses unsure about the security of their web applications, mobile apps, APIs or infrastructure, an initial security discussion can be the first step toward understanding their actual exposure.
Organizations and technology partners can explore COVBEC’s cybersecurity capabilities or discuss their security requirements at info@covbec.com
COVBEC LLP — Built To Break Threats.